ServicesStrategy & Governance

Know your data. Lock down what matters. Make AI safe to adopt.

Before Copilot and AI agents start reading everything, find out where your sensitive data really lives. We discover it, label it, lock it down and hand you the evidence your board and auditors ask for.

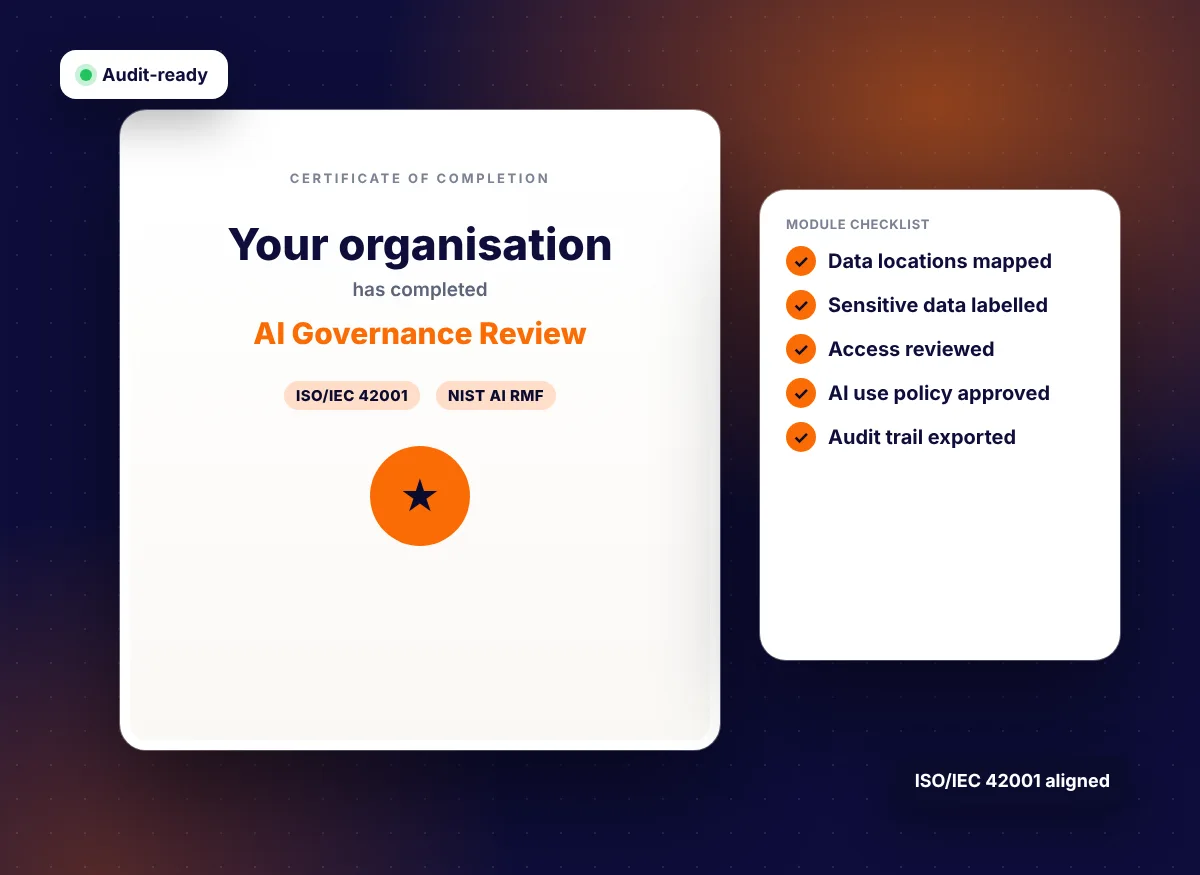
ISO/IEC 42001 alignedNIST AI RMFMicrosoft Purview syncShadow-AI discovery
Running
24/7 monitored
ISO 42001aligned controls
27001and NIST CSF mapping
100%audit trail on every move
2-4 wksfirst readiness report
What it is

Find what matters, label it and move it somewhere safe

An enterprise data-governance service that finds sensitive data, labels it and moves it somewhere safe, before AI tools, copilots and agents can expose it. It also covers data readiness: audit, classification and quality checks so your business is ready before using AI.

The service supports alignment with these frameworks. It does not constitute certification, which remains with accredited certification bodies.

Find, label and protect sensitive data
01

Scan

Structured sources and unstructured data (file shares, SharePoint/OneDrive, Google Drive, email archives, S3/Blob) for critical data elements.

02

Label

Sensitivity labels for PII, financial, health, IP and credentials, synced with Microsoft Purview.

03

Quarantine

Move sensitive items to secure locations with access controls, retention rules and a full audit trail.

04

AI governance

AI system inventory, risk register, impact assessments, policy library and shadow AI discovery.

05

Framework mapping

ISO/IEC 42001, ISO/IEC 27001, NIST AI RMF and NIST CSF, supporting Privacy Act and APP alignment.

06

Board-ready reporting

Dashboards for the board, CISO and DPO, and evidence packs for auditors.
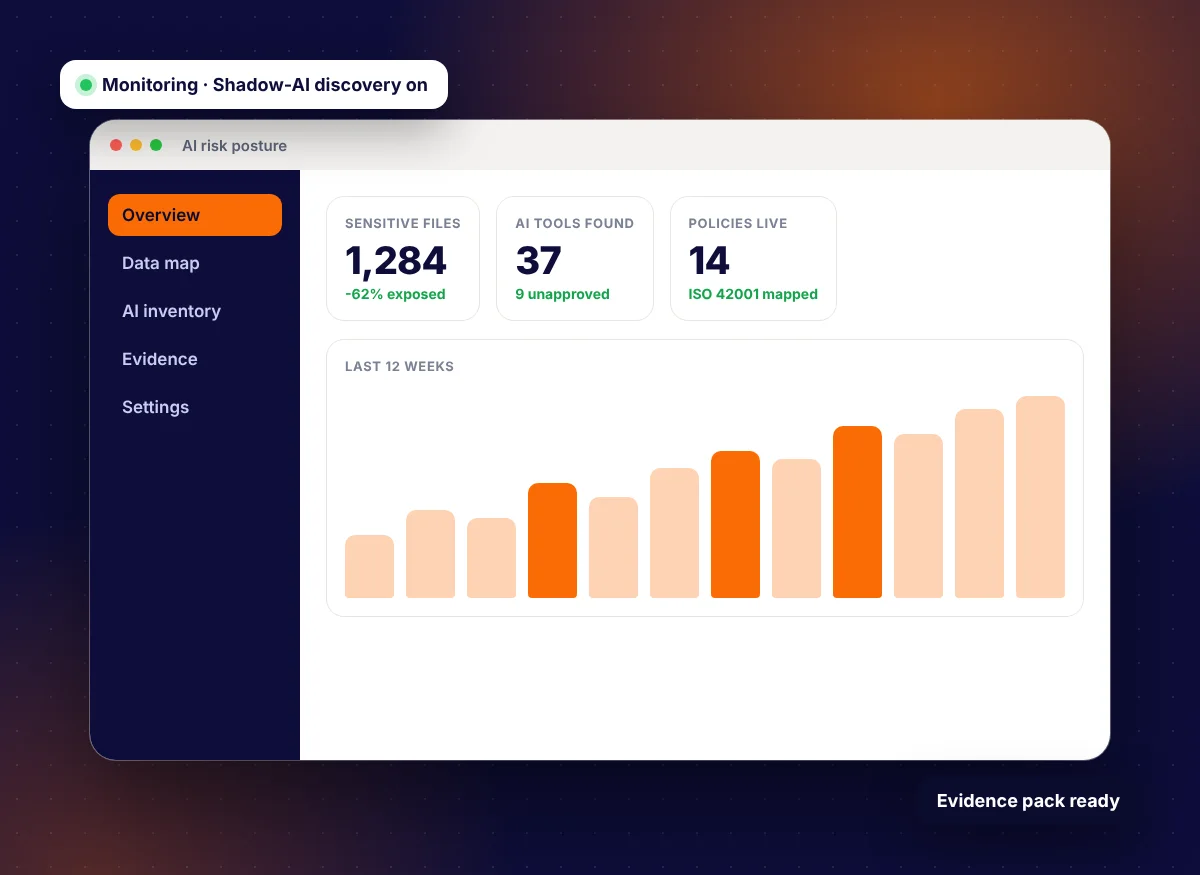
Know where AI risk sits, with numbers
Evidence your board and auditors can trust
Typical use cases

Where AI & Data Governance makes the difference

01

Copilot readiness

Find and fix over-shared files before Microsoft Copilot or any AI assistant can surface them to the wrong people.

02

Shadow-AI discovery

See which AI tools staff already use, what data goes into them and which ones need an approved alternative.

03

Policy that people follow

Short, plain-English AI use rules mapped to ISO/IEC 42001 and the Privacy Act, with training attached.

04

Audit and board reporting

One evidence pack showing risks, controls and ownership, ready for auditors, insurers and directors.

Live workflow · Governance workflow

From unknown data to audit-ready evidence

Watch how sensitive data is discovered, labelled, locked down and reported. Each step lights up as it runs.

Governance workflow
Running
Schedule TriggerNightly scan
Scan locationsSharePoint, Drive, S3
Classify dataRules + ML
Contains PII?Filter
Apply labelPurview sync
QuarantineSecure vault
Update risk registerData table
Notify DPOSlack / Email
Build evidence packEdit Fields
1
ScanSharePoint, Drive, S3, email
2
ClassifyPolicy rules plus ML
3
LabelPurview label sync
4
QuarantineSecure vault, audit log
5
AI risk checkInventory and shadow AI
6
EvidenceBoard and auditor packs
Governance run · finance share
  1. Scanning 48,210 files across 3 locations…
  2. 312 items contain personal or financial data.
  3. Labels applied: Confidential – Finance.
  4. Moved to secure vault. Access narrowed to 6 people.
  5. Shadow AI tool found in 2 teams. Added to the register.
  6. Audit evidence pack generated.
Modern stack

Tools and standards we use

We choose what fits your risk and budget rather than locking you into one vendor.

Microsoft PurviewSensitivity labels and data protection
ISO
ISO/IEC 42001AI management system standard
ISO
ISO/IEC 27001Information security management
NIST AI RMFRisk and cybersecurity frameworks
OWASP LLM Top 10Prompt injection and LLM risks
Privacy Act & APPsAustralian privacy alignment
Great ExpectationsAutomated data quality tests
dbtTested, documented models
What you get

Clear deliverables, no surprises

  • Sensitive data map and classification rules
  • Labelling and access clean-up plan
  • AI inventory and risk register
  • AI use policy and approval workflow
  • Board and audit evidence pack
  • Staff briefing and quick-reference guide
Typical timeline

From kick-off to live

Week 1Scope, systems access and discovery scan
Week 2Findings, risk ranking and quick wins
Weeks 3-4Labelling, policy and controls in place
Week 5Evidence pack and handover

Timelines depend on scope and access to your systems. Your fixed-scope plan confirms exact dates.

Who it is for

Built for the people who own the problem

Ideal buyer

CISOs, CIOs, DPOs, risk and compliance leaders preparing for Copilot or AI roll-outs, and organisations facing audits.

Questions we start with

  • Do you know where sensitive unstructured data lives?
  • Who can access it today?
  • What happens when an AI assistant indexes it?
  • What does your AI inventory look like?

Results we measure

  • Sensitive items found and remediated
  • Over-shared files reduced
  • Labelled-data coverage %
  • Time to audit evidence
Pricing

Choose the plan that fits

Each plan has a one-time setup fee and a monthly subscription covering hosting, monitoring, updates and support. Pay annually and get 2 months free.

Individual / Professional

Sole traders, consultants and small teams

Setup (one-time)A$990
MonthlyA$79/mo
  • Up to 100 GB scanned, 1 data source
  • PII and financial discovery
  • AI-use policy template
  • Email support, 2 business days
Get started
Most popular

Business

SMEs and growing teams

Setup (one-time)A$24,900
MonthlyA$2,500/mo
  • Up to 5 data sources, 5 TB
  • Policy-based classification and labelling
  • AI inventory and policy pack
  • ISO 27001 and NIST CSF mapping
  • 99.9% uptime, 4-hr response
Book a consultation

Enterprise

Large, multi-team or regulated organisations

Setup (one-time)from A$120,000
Monthlyfrom A$14,000/mo
  • Unlimited, hybrid and multi-cloud sources
  • Custom models and multi-label taxonomy
  • ISO/IEC 42001 management-system build-out
  • Live multi-entity dashboards
  • Named TAM, 24x7 option
Request a scoped quote

All prices in AUD and exclude GST. Enterprise is “from” pricing; a scoped quote follows discovery. Third-party licences are billed at cost plus handling. Minimum term 12 months for monthly subscriptions.

How we work

From first call to running in production

01

Free consultation

We listen, review your context and agree the goals. No obligation.

02

Tailored proposal

A clear scope, plan and price you can take to your team.

03

Build and test

We deliver in short cycles with your team in the loop.

04

Launch and run

Go live, monitor, and keep improving under your SLA.

Common questions

Does this certify us against ISO/IEC 42001 or ISO/IEC 27001?

No. The service supports alignment with these frameworks but does not constitute certification. Certification remains with accredited certification bodies.

What kinds of data can you scan?

Structured sources and unstructured data such as file shares, SharePoint/OneDrive, Google Drive, email archives, S3/Blob and chat exports.

Do we need Microsoft Purview?

No. We use it where you already license it, and lighter tools or manual processes where you do not.

How long does a first audit take?

A first readiness report typically takes two to four weeks, depending on how many systems are in scope.

Ready to make AI safe to adopt?

Book a free consultation. No obligation, response within 24 hours.
  • Free situation and requirements analysis
  • Fixed-scope plan and transparent pricing
  • Reply from a real person within 24 hours

Quick enquiry

Or use the full form below. We never share your details.

Talk to us about AI & Data Governance

  • Non-binding initial consultation
  • Free situation and requirements analysis
  • Response within 24 hours
Zoya Khan, Head of Strategy & Sales
Zoya KhanHead of Strategy & Sales

Your message